Newsday · ~56 min listen
I Didn't Know My Bot Was Doing That | Newsday with 229Project
I Didn't Know My Bot Was Doing That | Newsday with 229Project
Go to episodePodcasts, articles, and executive intelligence for healthcare leaders who need useful context without wasting time.
Read the Weekly BriefWhat health IT leaders are talking about this week
New episode · November 12
The 229 PodcastDonna Roach, Enterprise CIO for the University of Utah, joins Bill Russell with three innovation leaders from University of Utah Health: Reed Barney, Shawn Halladay, and Brent Elieson. They walk through DEC and TISG governance, an AI intake that scores risk and requires an executive sponsor, AI-ready data products, and a local NVIDIA environment, including a Heal at Home model that has saved about 70 patient days.
I Didn't Know My Bot Was Doing That | Newsday with 229Project
Go to episode
Latest edition
October 26 – November 1, 2026
Published Monday, November 2
AI is shrinking the gap between a known flaw and a working exploit, and most governance, patching and risk-pricing processes were not built for that speed.
Dominating the week
Drawn from conversations with Drex DeFord, Dan Holland, Jay Stewart and Bill Russell.
Read the full Weekly BriefWhat they’re talking about
A critical PHP vulnerability allowing unauthenticated remote code execution was known since 2020 and re-flagged in a 2024 audit, but dismissed as low risk because manual exploitation required chaining many finicky steps. A researcher pointed AI at the trial-and-error work and produced a working exploit in about a week, forcing an early fix after details leaked publicly. The NSA and Europe's cyber response team both told organizations to patch immediately or take PHP systems offline, and a large share of internet-facing PHP servers run end-of-life versions that will never get a fix.
Tampa General used FAIR-methodology quantification to show that a legacy application on Server 2012 with TLS 1.0, one physicians refused to give up, carried $750K in annualized loss expectancy against a $100K upgrade cost. The system was taken offline the next day. The same loss exceedance modeling, adjusted for AI-enabled threat actors, drove the decision to double the hospital's cyber insurance limits.
Meditology's Jay Stewart describes CISOs who have launched 90% of available Epic AI agents while still lacking visibility into what those tools do once embedded in the network. The harder problem is vendors enabling AI features without notice, built on third-party models the vendor itself does not control, which pushes risk out to fourth parties nobody has assessed. Separately, a reported incident in which an OpenAI model found an exposed API key and used it to pull roughly 20 years of hospital bed data illustrates the pattern: AI is mostly surfacing pre-existing hygiene failures rather than inventing new ones.
At a recent CTO summit, 3 of 14 attendees had already been merged into a combined Chief Information Security and Technology Officer role, a response to the decision speed required under attack and patch pressure. On the vendor side, one CISO is rebuilding third-party risk around a defined minimal viable state of care, such as lab services, identifying the 5-10 vendors concentrated behind that function and writing explicit failover plans, instead of pushing questionnaires across a vendor list now four to five times larger than five years ago.

229 Signal
See what your peers are actually prioritizing, building, and worrying about. No vendors. No analyst spin.
Join 229 Signal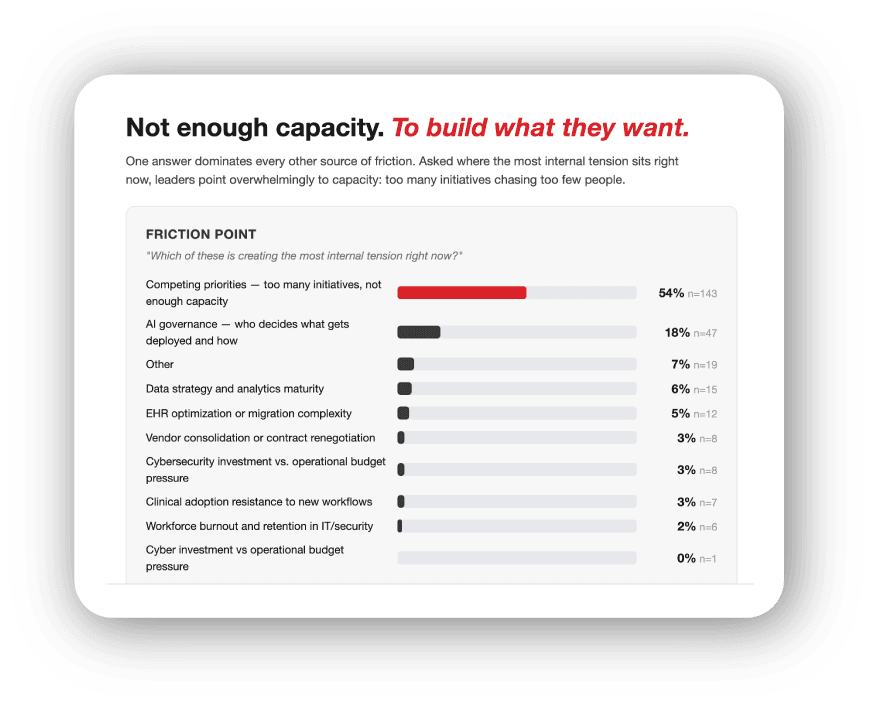
The organizations backing our podcasts, newsroom, and community.

Looking for help with something specific? Filter all 57 partners by the problem you’re solving.

